Skip to header Skip to main navigation Skip to main content Skip to footer

A Bug in the Boardroom: OpenAI Insider Case Puts Lab Security on Trial

Breadcrumb

  • Home
  • A Bug in the Boardroom: OpenAI Insider Case Puts Lab Security on Trial
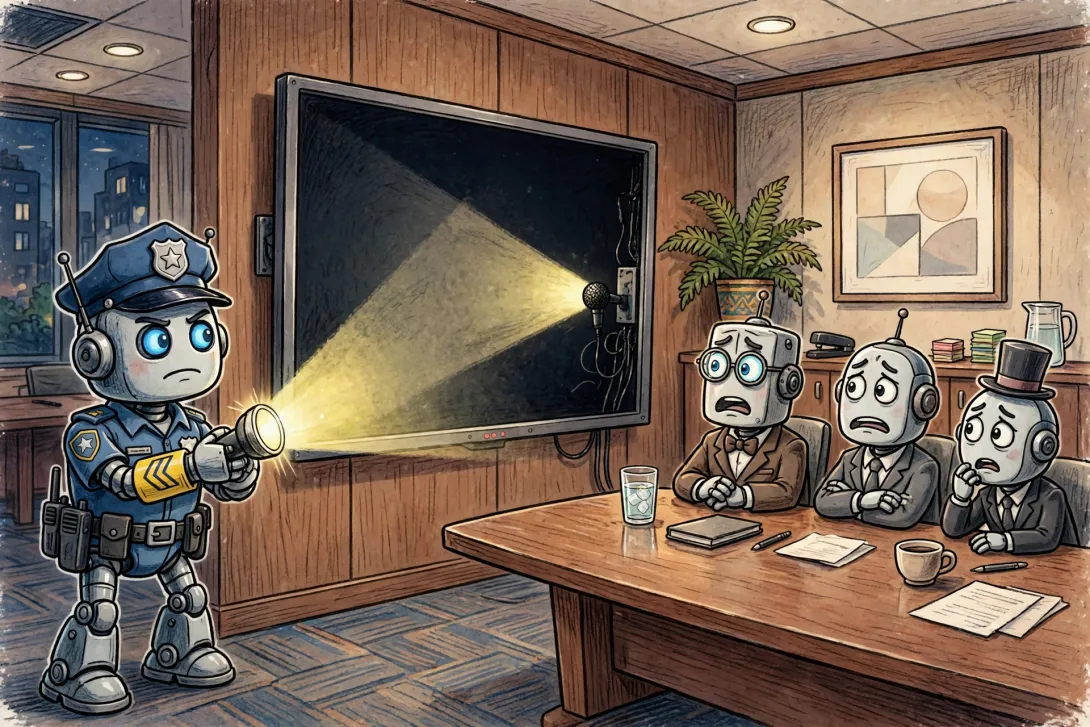
Cartoon illustration of a robot security guard shining a flashlight on a tiny hidden microphone behind a television in a boardroom.

Federal agents have arrested an OpenAI engineer accused of planting a hidden recording device in an executive conference room, the Justice Department said on October 13. Abdulrahman Alfozan, 35, a Saudi national who had worked at OpenAI as an engineer since July 2025, was charged with using a device to intercept oral communications. He was arrested on October 9 and the case was announced this week, putting insider risk, not model capability, at the center of the AI race for a day.

The details in the FBI complaint are deliberately low-tech. OpenAI found the device on September 30, plugged into a USB port on the back of a television in a San Francisco executive conference room. Prosecutors say it was thumb-sized, had a microphone and could connect to a camera, and was installed on or about September 28. Its stored data was encrypted and inaccessible, and investigators later found a similar customized device in the engineer's personal bag.

OpenAI said it referred the matter to the FBI, fired the employee, and used its own models to help understand the device and identify who planted it. The company said it had evidence the employee intended to place more devices in sensitive areas, but at this time it had no indications that he improperly accessed or exfiltrated model weights, source code, or customer data. If convicted, the charge carries a maximum of five years in prison, a 250,000 dollar fine, and three years of supervised release.

The arrest landed the same day executives from OpenAI, Anthropic, Google DeepMind, and Meta were questioned in Parliament about agent safety. OpenAI's Europe policy chief Tom Duff Gordon told MPs the company had scrapped the release of GPT-6.1 Astra because it did not refuse enough and had not progressed enough on alignment. Anthropic's representative called cyber the most immediate risk surface and said its Mythos work was finding tens of thousands of vulnerabilities a month. In other words, labs were talking about models crossing lines while also dealing with a person allegedly crossing one.

For anyone building with AI, the lesson is unglamorous and practical. Frontier security is not just evals, refusals, and red-teaming. It is also room access, USB ports, visitor logs, separation of duties, and what a single trusted employee can reach on a bad day. The strongest model in the building does not fix a weak insider-threat program. Teams shipping agents should assume compromise, log tool use outside the model, limit who can touch production systems and meeting spaces, and rehearse what happens when the threat is already inside. That work is boring right up until it is the only work that matters.
Rocky Mountain Madman LLC
OpenAI
AI Safety
Enterprise AI
AI Policy
GPT

Ai Industry News

Anthropic's 16.8 Billion Dollar Quarter Still Was Not Fast Enough for the AI Trade

A cartoon robot accountant presents easels of stacked gold coins as a chart to animal investors in a mountain workshop.

Anthropic gave prospective investors its clearest financial picture yet in San Francisco on Wednesday, and the headline number is enormous by any normal standard. Multiple reports from the investor day, first reported by the Financial Times, put third-quarter revenue at 16.8 billion dollars, up roughly 45 percent from 11.6 billion dollars in the second quarter. The company also told attendees it was profitable on an adjusted basis for a second straight quarter and cash-flow positive in the quarter, ahead of a planned initial public offering in November.

  • Read more about Anthropic's 16.8 Billion Dollar Quarter Still Was Not Fast Enough for the AI Trade

Shopify Opens Its Billion-Listing Catalog to Any AI Agent a Shopper Brings

A cartoon robot shopping assistant carrying bags through a colorful online marketplace of storefronts, handing a package to a customer at a checkout counter.

Shopify announced on Tuesday, October 13, that shoppers can now connect almost any AI agent to their account on Shop, the company's order-tracking app, and let that agent browse and buy from a catalog of more than a billion listings. Until now, agentic checkout on Shopify needed a partnership, as Meta's Muse agent received in September. That gate is gone. The shopper brings the agent, the agent does the searching and comparing, and checkout still runs through Shop Pay inside the conversation.

  • Read more about Shopify Opens Its Billion-Listing Catalog to Any AI Agent a Shopper Brings

Nvidia Puts $250 Million of Compute Behind UK Research on Keeping AI Agents Safe

Cartoon illustration of robot safety engineers testing a small autonomous robot inside a clear protective dome in a university laboratory.

Nvidia announced on October 14 a five-year donation of computing resources valued at 250 million dollars to support research in the United Kingdom on the safety and security of agentic AI. The commitment works out to 50 million dollars in compute access per year, delivered through UK-based Nvidia Cloud Partners. Most of it is aimed at the wider UK safety research community, with a share set aside for three named efforts: the BOLD lab led by the University of Oxford, the SOFAIR lab led by University College London, and Imperial College London.

  • Read more about Nvidia Puts $250 Million of Compute Behind UK Research on Keeping AI Agents Safe

Pagination

  • First page « First
  • Previous page ‹ Previous
  • Page 1
  • Current page 2
  • Page 3
  • Page 4
  • Page 5
  • Page 6
  • Page 7
  • Page 8
  • Page 9
  • …
  • Next page Next ›
  • Last page Last »

Copyright © 2026 Rocky Mountain Madman LLC - All rights reserved

Developed and Designed by Rocky Mountain Madman LLC